n8n 'Configured to Use a Secure Cookie' Warning Behind nginx: Redirect HTTP to HTTPS
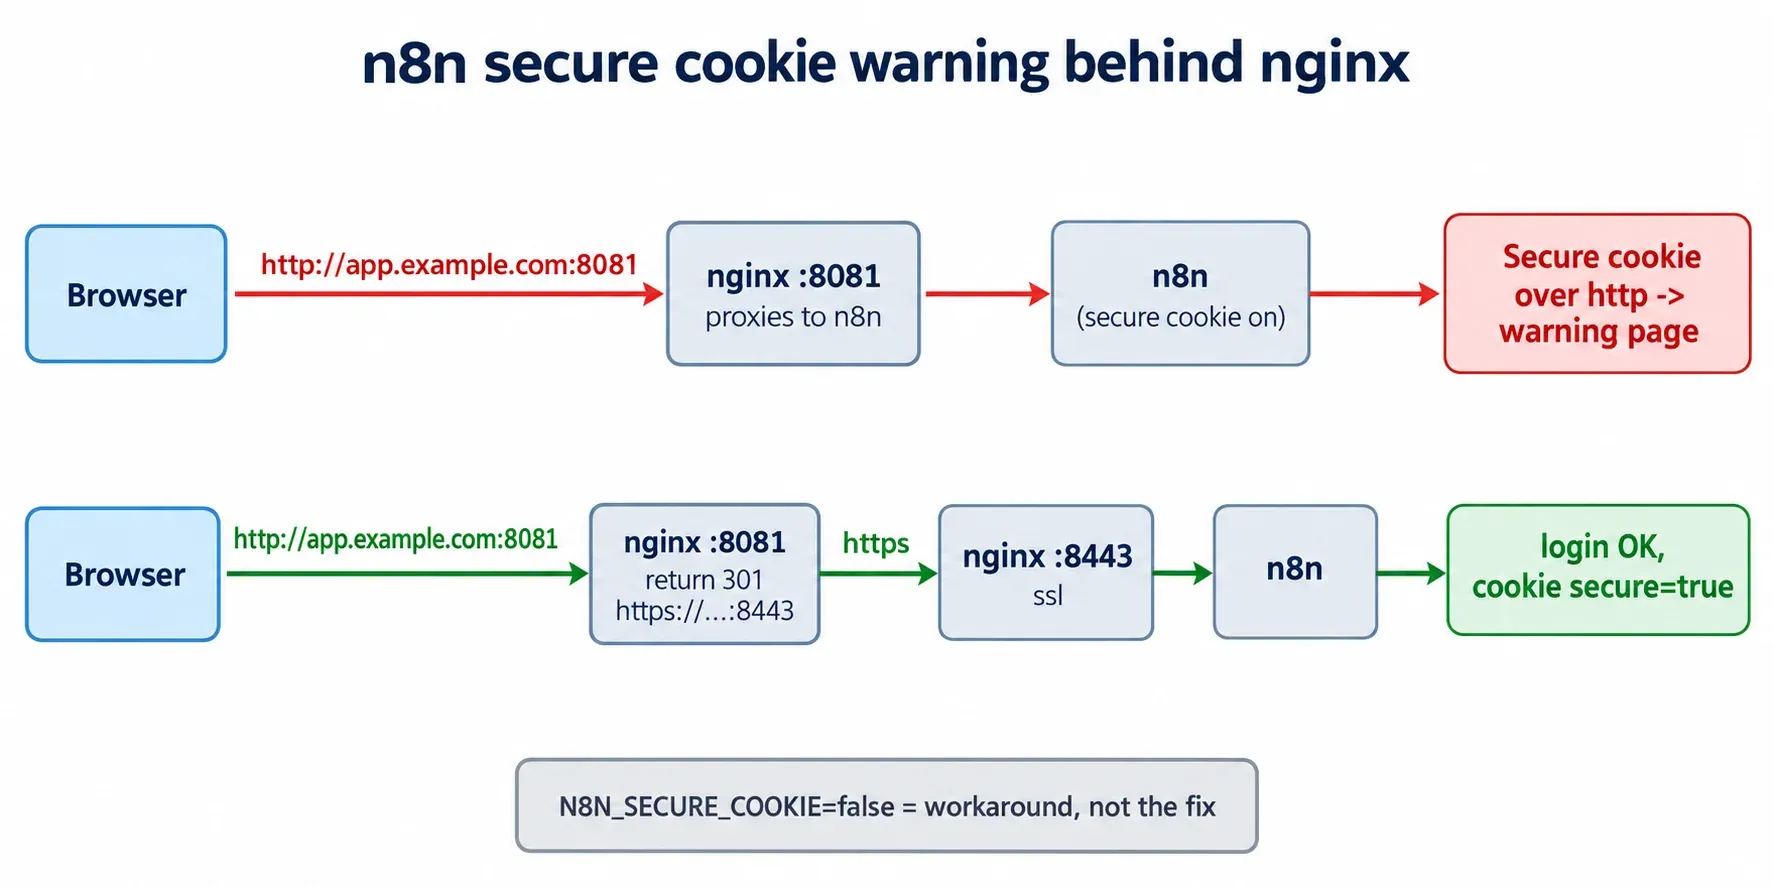
Your n8n server is configured to use a secure cookie, however you are either visiting this via an insecure URL, or using Safari.Short answer: Opening n8n over plain HTTP through nginx (http://repro.local:8081/) showed the full-page secure cookie warning, because n8n's auth cookie is Secure by default. A 301 from the HTTP server block to the HTTPS listener fixed it in all toggle rounds. Removing X-Forwarded-Proto on HTTPS did not trigger the warning in our test. N8N_SECURE_COOKIE=false also hides it, but that is a workaround, not a fix.
Symptom
When nginx proxies plain HTTP requests on port 8081 directly to n8n (3-broken.conf) and you open http://repro.local:8081/ in a browser, n8n does not render the sign-in form. Instead, it displays a full-page warning with the exact text:
“Your n8n server is configured to use a secure cookie, however you are either visiting this via an insecure URL, or using Safari.”
To fix this, please consider the following options:
- Setup TLS/HTTPS (recommended), or
- If you are running this locally, and not using Safari, try using localhost instead
- If you prefer to disable this security feature (not recommended), set the environment variable N8N_SECURE_COOKIE to false
In this broken state (3-broken), the server responds with 200 text/html; charset=utf-8, /rest/settings reports "authCookie":{"secure":true}, and the browser probe stops at http://repro.local:8081/signin?redirect=%252F with secureCookieWarning: true and 0 WebSockets opened:
===== 3-broken
nginx: the configuration file /etc/nginx/nginx.conf syntax is ok
nginx: configuration file /etc/nginx/nginx.conf test is successful
2026/10/29 17:55:56 [notice] 336#336: signal process started
active=# state: 3-broken.conf served=# state: 3-broken.conf
--- A probe http
{"label":"3-broken","secureCookieWarning":true,"finalUrl":"http://repro.local:8081/signin?redirect=%252F","wsCount":0,"ws":[]}
--- B server view
200 text/html; charset=utf-8
"authCookie":{"secure":true}
finalUrl http://repro.local:8081/signin?redirect=%252F
[]
Confirm Which Layer
To verify what actually triggers the warning page—and rule out common misconceptions—we ran four controls against the exact same n8n 2.44.7 instance:
- Control B (
3-localhost— direct HTTP on127.0.0.1:5679): Openinghttp://127.0.0.1:5679/directly in Chromium shows no warning, login returns200, push WebSockets succeed, and the cookie retainssecure=true(Chromium treats127.0.0.1as a secure context). - HTTPS Control (
3-https— via nginx onhttps://repro.local:8443/): Opening the HTTPS listener directly shows no warning and login returns200. - Myth Control C (
3-no-xfp— HTTPS with0X-Forwarded-Protolines in nginx): A claim we tested is that missingX-Forwarded-Protoin nginx causes the secure cookie warning page even when visiting over HTTPS. We testedhttps://repro.local:8443/using3-control-no-xfp.conf(X-Forwarded-Proto set lines in served conf: 0). Result: no warning, login200, push WebSockets OK, and cookiesecure=true. MissingX-Forwarded-Protodoes not cause this page:
===== 3-no-xfp (myth control)
nginx: the configuration file /etc/nginx/nginx.conf syntax is ok
nginx: configuration file /etc/nginx/nginx.conf test is successful
2026/10/29 17:58:53 [notice] 424#424: signal process started
active=# state: 3-control-no-xfp.conf served=# state: 3-control-no-xfp.conf
X-Forwarded-Proto set lines in served conf: 0
{"label":"3-no-xfp","secureCookieWarning":false,"loginStatus":200,"finalUrl":"https://repro.local:8443/signin?redirect=%252F","postLoginUrl":"https://repro.local:8443/assistant","editorUrl":"https://repro.local:8443/workflow/UCxBiJ4TRJmiTuqO","wsCount":2,"connectionLostVisible":false,"ws":[{"url":"wss://repro.local:8443/rest/push?pushRef=vuc8jg8vjb","frames":[],"closed":false},… (truncated)
cookies [{'name': 'n8n-auth', 'secure': True, 'sameSite': 'Lax', 'domain': 'repro.local'}]- Workaround Control D (
3-securecookie-false—N8N_SECURE_COOKIE=falseover plain HTTP): SettingN8N_SECURE_COOKIE=falseon the n8n container changes/rest/settingsto"authCookie":{"secure":false}and suppresses the warning overhttp://repro.local:8081/(loginStatus: 200, push OK overws://, cookiesecure: False). This is a workaround that bypasses the check, not the fix: n8n’s own warning page labels it “(not recommended)”, and the cookie is no longer markedSecure:
===== 3-securecookie-false (workaround control)
nginx: the configuration file /etc/nginx/nginx.conf syntax is ok
nginx: configuration file /etc/nginx/nginx.conf test is successful
2026/10/29 17:59:38 [notice] 453#453: signal process started
nginx: the configuration file /etc/nginx/nginx.conf syntax is ok
nginx: configuration file /etc/nginx/nginx.conf test is successful
2026/10/29 17:59:40 [notice] 475#475: signal process started
active=# state: 3-broken.conf served=# state: 3-broken.conf
 Container repro-n8n-b2-n8n-1 Started
false
"authCookie":{"secure":false}
{"label":"3-securecookie-false","secureCookieWarning":false,"loginStatus":200,"finalUrl":"http://repro.local:8081/signin?redirect=%252F","postLoginUrl":"http://repro.local:8081/assistant","editorUrl":"http://repro.local:8081/workflow/UCxBiJ4TRJmiTuqO","wsCount":2,"connectionLostVisible":false,"ws":[{"url":"ws://repro.local:8081/rest/push?pushRef=h2zrkc4sq8","frames":[],"closed":false},… (truncated)
cookies [{'name': 'n8n-auth', 'secure': False, 'sameSite': 'Lax', 'domain': 'repro.local'}]
 Container repro-n8n-b2-n8n-1 Started
nginx: the configuration file /etc/nginx/nginx.conf syntax is ok
nginx: configuration file /etc/nginx/nginx.conf test is successful
2026/10/29 18:01:05 [notice] 497#497: signal process started
active=# state: 3-fixed.conf served=# state: 3-fixed.conf
restored N8N_SECURE_COOKIE=(unset)
"authCookie":{"secure":true}
Cause
In 3-broken.conf, the plain-HTTP server block (listen 8081;) proxies requests directly to http://n8n:5678 instead of redirecting the browser to the HTTPS listener (listen 8443 ssl;):
# state: 3-broken.conf
server {
  listen 8081;
  server_name repro.local;
  location / {
    proxy_pass http://n8n:5678;
    proxy_http_version 1.1;
    proxy_set_header Upgrade $http_upgrade;
    proxy_set_header Connection "upgrade";
    proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
    proxy_read_timeout 3600s;
    proxy_set_header Host $http_host;
    proxy_set_header X-Forwarded-Proto $scheme;
  }
}
server {
  listen 8443 ssl;
  server_name repro.local;
  ssl_certificate     /etc/nginx/certs/repro.crt;
  ssl_certificate_key /etc/nginx/certs/repro.key;
  location / {
    proxy_pass http://n8n:5678;
    proxy_http_version 1.1;
    proxy_set_header Upgrade $http_upgrade;
    proxy_set_header Connection "upgrade";
    proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
    proxy_read_timeout 3600s;
    proxy_set_header Host $http_host;
    proxy_set_header X-Forwarded-Proto $scheme;
  }
}
As general browser and HTTP mechanism knowledge (consistent with the controls measured above):
- By default in n8n,
N8N_SECURE_COOKIEis enabled ("authCookie":{"secure":true}in/rest/settings), meaning then8n-authsession cookie carries theSecureattribute. - Browsers generally only set and send
Securecookies over secure contexts (https://; Chromium also treats loopback such as127.0.0.1as secure, which matches Control B). - When a user visits
http://repro.local:8081/(a non-localhosthttp://origin) and nginx proxies that plain-HTTP request straight to n8n, the frontend (inferred; we did not read the frontend code) detects that the server requires a secure cookie ("authCookie":{"secure":true}) while the browser is on an insecure URL, and renders the warning page.
The One Change
Replace the proxy_pass block inside the HTTP server block (listen 8081;) with a 301 redirect to the HTTPS listener (https://$host:8443$request_uri) and reload nginx:
The diff below is derived by comparing 3-broken.conf and 3-fixed.conf:
 server {
   listen 8081;
   server_name repro.local;
   location / {
-    proxy_pass http://n8n:5678;
-    proxy_http_version 1.1;
-    proxy_set_header Upgrade $http_upgrade;
-    proxy_set_header Connection "upgrade";
-    proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
-    proxy_read_timeout 3600s;
-    proxy_set_header Host $http_host;
-    proxy_set_header X-Forwarded-Proto $scheme;
+    return 301 https://$host:8443$request_uri;
   }
 }
Verify
With 3-fixed.conf active, our curl check (the requested path is not printed in the captured output) returned HTTP/1.1 301 Moved Permanently with Location: https://repro.local:8443/home/workflows. The browser follows the redirect to https://repro.local:8443/..., logs in with loginStatus: 200 and secureCookieWarning: false, sets the n8n-auth cookie with 'secure': True, and keeps the wss:// push WebSocket open:
===== 3-fixed
nginx: the configuration file /etc/nginx/nginx.conf syntax is ok
nginx: configuration file /etc/nginx/nginx.conf test is successful
2026/10/29 17:57:32 [notice] 358#358: signal process started
active=# state: 3-fixed.conf served=# state: 3-fixed.conf
HTTP/1.1 301 Moved Permanently
Location: https://repro.local:8443/home/workflows
{"label":"3-fixed","secureCookieWarning":false,"loginStatus":200,"finalUrl":"https://repro.local:8443/signin?redirect=%252F","postLoginUrl":"https://repro.local:8443/assistant","editorUrl":"https://repro.local:8443/workflow/UCxBiJ4TRJmiTuqO","wsCount":2,"connectionLostVisible":false,"ws":[{"url":"wss://repro.local:8443/rest/push?pushRef=c5p9brl24i","frames":[],"closed":false},… (truncated)
cookies [{'name': 'n8n-auth', 'secure': True, 'sameSite': 'Lax', 'domain': 'repro.local'}]
Toggling between 3-broken.conf and 3-fixed.conf (3-broken → 3-fixed → 3-broken-again → 3-fixed-again) confirmed the behavior across all rounds:
===== 3-broken-again
nginx: the configuration file /etc/nginx/nginx.conf syntax is ok
nginx: configuration file /etc/nginx/nginx.conf test is successful
2026/10/29 17:58:04 [notice] 380#380: signal process started
active=# state: 3-broken.conf served=# state: 3-broken.conf
{"label":"3-broken-again","secureCookieWarning":true,"finalUrl":"http://repro.local:8081/signin?redirect=%252F","wsCount":0,"ws":[]}

===== 3-fixed-again
nginx: the configuration file /etc/nginx/nginx.conf syntax is ok
nginx: configuration file /etc/nginx/nginx.conf test is successful
2026/10/29 17:58:21 [notice] 402#402: signal process started
active=# state: 3-fixed.conf served=# state: 3-fixed.conf
{"label":"3-fixed-again","secureCookieWarning":false,"loginStatus":200,"finalUrl":"https://repro.local:8443/signin?redirect=%252F","postLoginUrl":"https://repro.local:8443/assistant","editorUrl":"https://repro.local:8443/workflow/UCxBiJ4TRJmiTuqO","wsCount":2,"connectionLostVisible":false,"ws":[… (truncated)
Summary of All Tested States and Controls
| State | URL | Result |
|---|---|---|
3-broken |
http://repro.local:8081/ |
warning=true (full page); server 200 text/html, /rest/settings → "authCookie":{"secure":true} |
3-localhost (Control B) |
http://127.0.0.1:5679/ |
no warning, login 200, push OK, cookie secure=true (Chromium treats 127.0.0.1 as secure context) |
3-https (Control) |
https://repro.local:8443/ |
no warning, login 200 |
3-fixed |
http://repro.local:8081/ |
HTTP/1.1 301 Location: https://repro.local:8443/home/workflows; probe ends on https, warning=false, login 200, n8n-auth secure=true |
3-broken-again / 3-fixed-again |
http://repro.local:8081/ |
warning=true / warning=false, login 200 |
3-no-xfp (Myth, Control C) |
https://repro.local:8443/ with 0 X-Forwarded-Proto lines in served conf |
no warning, login 200, push OK, cookie secure=true → missing XFP does NOT cause this page |
3-securecookie-false (Control D) |
http://repro.local:8081/ + N8N_SECURE_COOKIE=false |
no warning, login 200, push OK over ws://, cookie secure=false (a workaround; n8n’s own page labels it “not recommended”); env restored, settings back to secure=true |
Minimal Working Config
# state: 3-fixed.conf
server {
  listen 8081;
  server_name repro.local;
  location / {
    return 301 https://$host:8443$request_uri;
  }
}
server {
  listen 8443 ssl;
  server_name repro.local;
  ssl_certificate     /etc/nginx/certs/repro.crt;
  ssl_certificate_key /etc/nginx/certs/repro.key;
  location / {
    proxy_pass http://n8n:5678;
    proxy_http_version 1.1;
    proxy_set_header Upgrade $http_upgrade;
    proxy_set_header Connection "upgrade";
    proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
    proxy_read_timeout 3600s;
    proxy_set_header Host $http_host;
    proxy_set_header X-Forwarded-Proto $scheme;
  }
}
Untested / Not Covered
- Safari-specific behavior on
localhost/127.0.0.1: All browser probes ran in Chromium (chromium-1248) via Playwright1.64.1; Safari (which the n8n warning text mentions alongside insecure URLs) was not tested. - Other effects of omitting
X-Forwarded-Proto: Control C verified only that omittingX-Forwarded-Protoonhttps://repro.local:8443/does not trigger the secure cookie warning page or break login/push WebSockets; other n8n features that might inspectX-Forwarded-Protowere not tested here.
Related
- n8n Behind nginx: ‘Connection lost’ and ‘Invalid origin!’ on a Non-Default Port: the next error you may hit on an HTTPS non-default port if nginx sends
Host $host. - n8n Webhook Returns 404 Behind nginx (Sub-Path Proxy): that config runs over plain HTTP with
N8N_SECURE_COOKIE=false, the workaround described in Control D.